I recently looked at the website of a company that itself sells cybersecurity services. In the browser, the site looked flawless. But the page source code, the code search engine crawlers read, contained a third-party ad block stuffed with links. In the visitor’s browser, a script removed that block straight away, so neither the staff nor the clients ever saw it. I wrote to the company and have not had a reply yet.
I’m not naming the company. If this happens to people who protect websites for a living, it can happen to you too. Below: how hidden spam on your website works, what you risk and how to look at your site through Google’s eyes in 10-15 minutes.
No time to deal with this?
I find the hidden spam, clean the files and database, close the entry point and send Google a review request. Cleanup from €100 excl. VAT, exact scope after diagnosis. If you’d rather check it yourself, everything is explained step by step below.
What it is and why an attacker wants it
SEO spam (spam SEO in French) is someone else’s text and links secretly added to your site to boost search rankings: casinos, medicines, counterfeits, loans.
Why your site? Your domain has a history and Google’s trust, which a brand-new casino site does not. So hacked sites are used as a platform: the links on them are sold or point to the attacker’s own pages. You pay for the hosting, and your site advertises for someone else.
In 2024, the free online scanner Sucuri SiteCheck detected 1,176,701 infected sites, and 38.4% of them had SEO spam; hidden blocks of text and links were found on 114,318 sites. This covers all CMSs, not just WordPress. The scanner looks at a site from the outside, like a visitor, so it can miss spam that is shown only to bots.
The Japanese spam I wrote about in Japanese spam in Google: how to check your site and what to do belongs to the same family. There it means thousands of new pages; here, a few links inside your ordinary pages.
How it is hidden
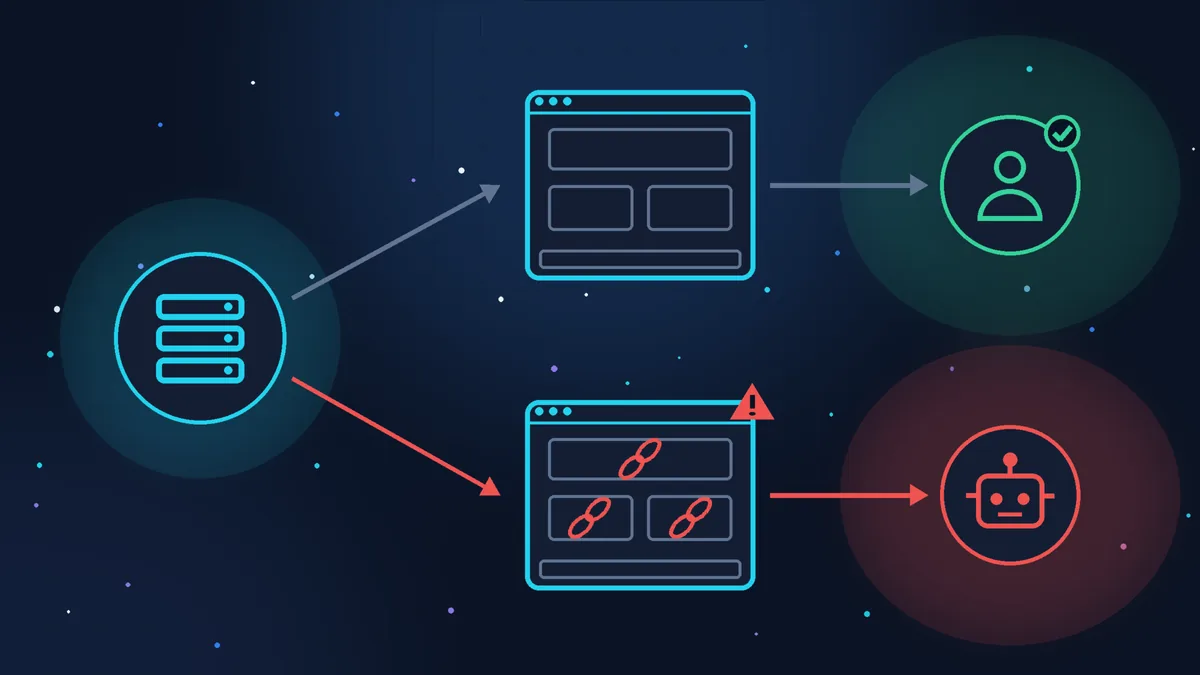
Google’s spam policies say: “If a site is hacked, it’s not uncommon for the hacker to use cloaking to make the hack harder for the site owner to detect.” Cloaking means showing different content to people and to robots. These are the techniques Sucuri describes:

Bots only
Browsers and robots identify themselves with a text string (the user agent). If Googlebot arrives, the code serves spam; if a person arrives, the normal page.

By Google’s address
Smarter code also checks the IP address (the computer’s address on the internet): only Google’s real servers get the spam.

Out of sight
The spam is in the code for everyone, but it is pushed off screen, made invisible (zero size, display:none) or removed by a script in the browser.

Not for the owner
People logged in to the admin area never see the spam. The code can also take other visitor details into account, such as where they came from.
This code lives in theme files, in WordPress core files that load every time a page opens, in the database (invisible in the admin area) and in .htaccess (the server settings in the site folder). That is why deleting a link in the page editor almost never helps.
What hidden spam puts at risk
- Rankings. Hidden text and links, cloaking and hacked content all violate Google’s spam policies. Google says such sites “may rank lower in results or not appear in results at all”.
- Issues in Search Console. Either automatically in the Security issues report (hack type “Hacked: Content injection”), or manually by a Google reviewer under Manual actions, for example “Site abused with third-party spam”.
- Reputation. Your clients don’t see the injected links, but Google, your partners and link-checking tools do.
- An open door. The attacker had access: today it’s links, tomorrow a redirect to a scam site.
How to check your site in 10-15 minutes
You need access to Google Search Console (Google’s free service for website owners). I explain how to set it up in Website not showing up on Google: how to find the cause step by step.
- Security issues and Manual actions. In the Search Console menu, find the Security issues and Manual actions reports. If there is an issue listed, the problem is confirmed: Google shows sample URLs, so go straight to “If you find something”.
- URL Inspection: the page through Google’s eyes. Paste your home page address into the search bar at the top of Search Console. Open “View crawled page”: this is the code the real Googlebot received on its last crawl. Then click “Test live URL” and “View tested page”: this fresh version is requested by a separate Google robot used for testing. In the code (HTML) of both versions, search (Ctrl+F or Cmd+F) for the words casino, viagra, cialis, pharmacy, loan, replica and for links to unfamiliar sites. The request comes from Google’s addresses, so this is the best way to spot IP-based cloaking. Repeat for 2-3 important pages.
- Google Search. Type
site:example.com casino(replace example.com with your own domain), then the same with viagra, bet, loan. No page should show unrelated words in its title or description. - The queries people find you with. In the Performance report, open the Queries tab. If a bakery’s site shows up for searches about betting or pills, that’s a warning sign.
- Comparison, for advanced users. You can request the page while identifying yourself as Google’s robot (replace example.com with your own domain).
On a Mac, in the Terminal app:
curl -sL -A "Googlebot" https://example.com/ | grep -i -o -E "casino|viagra|cialis|pharmacy"On Windows 10/11, in Command Prompt or PowerShell:
curl.exe -sL -A "Googlebot" https://example.com/ | findstr /i "casino viagra cialis pharmacy"If the words turn up, look at that page in URL Inspection: injected links around them almost certainly mean a hack. If nothing turns up, that proves nothing: the real Google robot is verified by its IP address, and clever code does the same.
Two tools won’t help here: the Links report (it shows links to your site, not from it) and Safe Browsing (it catches viruses and phishing, but usually not spam links).
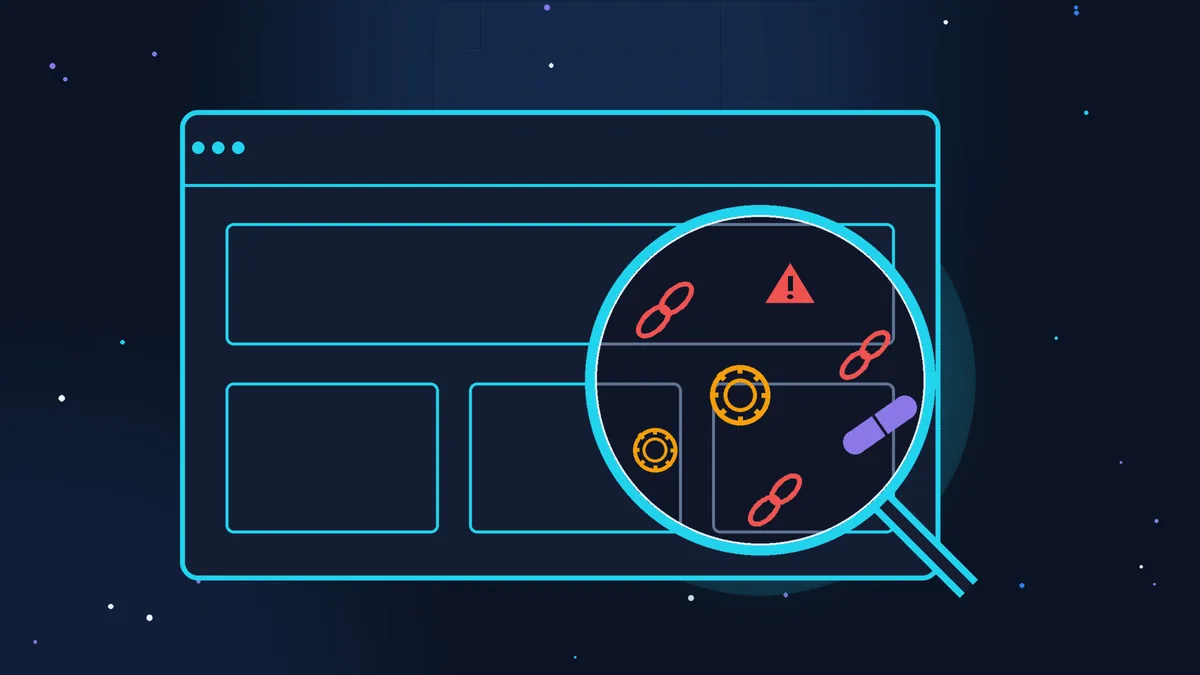
For clients on website maintenance, I check selected pages once a day with my own monitoring, on two levels: the page source code and what the visitor sees in the browser. For hidden spam, both matter: a block that a script removes for the visitor still shows in the source code, while content that a script swaps in afterwards shows in the browser. If even one word changes on a page or a new script appears, I know within 24 hours at most.
If you find something
- Keep evidence: screenshots, the words you found, the URLs.
- Make a full backup of the site (files and database) before changing anything.
- Change passwords: admin area, hosting, FTP/SFTP (file access). If you change the database password, you must also update it in the
wp-config.phpfile, otherwise the site will stop loading: if you don’t know where that is, leave this step to a specialist. Remove any unfamiliar administrators. - Find and remove the code in the theme, core, database and
.htaccess. It’s safer to reinstall the core, theme and plugins from clean copies. Any edits made directly in the theme will be lost, which is why the backup comes first. Don’t delete unfamiliar files at random. - Update everything and close the entry point (an old plugin, a leaked password).
- Ask Google to check again. If there was an issue under Security issues or Manual actions, click “Request Review” there and describe what you did. According to Google’s help, a review can take from a few days to a few weeks. If nothing was listed, use “Request indexing” in URL Inspection for your main pages.
If you don’t know where to start, France has a free government service, 17Cyber (in French), run by the police, the gendarmerie and Cybermalveillance.gouv.fr: diagnosis and advice, and a referral to a professional if needed.
Checklist
- repeat the check from the section above once a month and straight after anything odd: unrelated queries, spam complaint emails, a drop in traffic;
- admin, hosting and FTP passwords are unique, and there are no unfamiliar administrators;
- WordPress, the theme and plugins are up to date;
- there is a recent backup of the site you can restore from.
If your time is worth more
Any site owner can do steps 1-4 of the check, and they give an honest answer to the question “is there a problem?”. For other signs of a hack, see WordPress site hacked: the first warning signs.
If you would rather run your business than deal with a stranger’s code, Zen Webmaster will take care of the technical side: finding the cause, cleaning the files and database, closing the vulnerability and requesting a review from Google. Malware cleanup from €100 excl. VAT, exact scope after diagnosis.
Sources (checked 31/10/2026): Spam policies for Google web search, Google Search Central; Security issues report, Manual actions report, URL Inspection tool, Links report, Search Console Help; Verify requests from Google crawlers and fetchers, Google’s common crawlers, Google; SiteCheck 2024 Threat Report, Sucuri; Hiding Spam from Ahrefs and Majestic, Sucuri, 04/01/2016; Clever SEO Spam Injection, Sucuri, 17/12/2018; Google Sees Spam, You See Your Site, Sucuri, 08/01/2026; Fix the cloaked keywords and links hack, Google web.dev.
Rather not deal with it yourself?
Describe the task in a few words. I'll reply within one working day with what needs doing, the price and the timing.
Latest posts